|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> General >> CVS file existence information disclosure weakness Vulnerability Assessment Details
|
CVS file existence information disclosure weakness |
||
|
Logs into the remote CVS server and asks the version Detailed Explanation for this Vulnerability Assessment The remote CVS server, according to its version number, can be exploited by malicious users to gain knowledge of certain system information. This behaviour can be exploited to acertain the existence and permissions of arbitrary files and directories on a vulnerable system. Solution : Upgrade to CVS 1.11.17 and 1.12.9, or newer Network Security Threat Level: Low Networks Security ID: 10955 Vulnerability Assessment Copyright: This script is Copyright (C) 2004 David Maciejak |
||
|
Cables, Connectors |
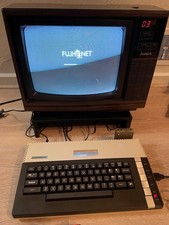
Fujinet 1.7.1 Atari 400 800 800XL 130XE 65XE XEGS Assembled, Tested, Working
$99.99
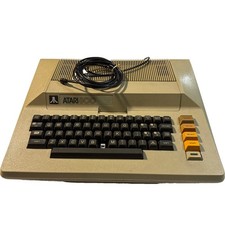
Atari 800 Home Computer For Parts Repair Untested Power Cord
$124.92
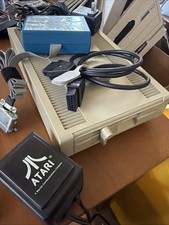
ATARI XF551 DISK DRIVE WITH AC POWER ADAPTER AND PARALLEL PORT ADAPTER, UNTESTED
$250.00
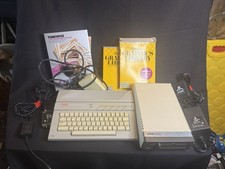
Atari 130 XE/Atari 1050 Bundle W/ Cords And Extras (Powered On)
$300.00
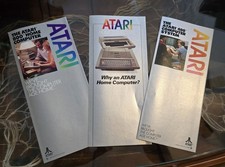
Vintage Atari 400/800 Home Computer Brochures – Set of 3 – $20
$20.00
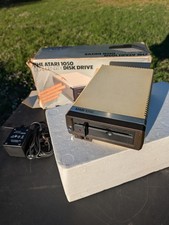
Vintage Atari 1050 Floppy Disk Drive w/ Power Adapter *Parts Only
$49.00
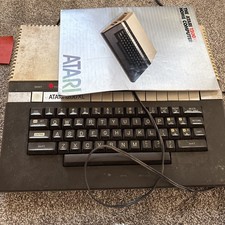
Vintage Atari 1200XL Home Computer Powers On, w owners guide and power supply
$250.00
SDrive Max Floppy Drive Emulator Atari 8-Bit 400/800/XL/XE Firmware 1.5 USB C R2
$70.00
Atari 1200XL Computer Game Console Vintage Rare BAD KEYBOARD MYLAR
$275.00
Atari 850 Interface Module Vintage 8-Bit Computer Expansion Serial Parallel Box
$159.95
|
||
|
No Discussions have been posted on this vulnerability. |