|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> General >> CVS pserver CVSROOT passwd file cmd exec Vulnerability Assessment Details
|
CVS pserver CVSROOT passwd file cmd exec |
||
|
Logs into the remote CVS server and asks the version Detailed Explanation for this Vulnerability Assessment The remote CVS server, according to its version number, might permit a possible hacker to execute arbitrary commands on the remote system as cvs does not drop root rights properly. Solution : Upgrade to CVS 1.11.11 Network Security Threat Level: High Networks Security ID: 9306 Vulnerability Assessment Copyright: This script is Copyright (C) 2003 Tenable Network Security |
||
|
Cables, Connectors |
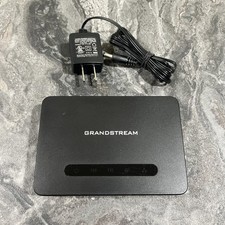
Grandstream HT813 VoIP Gateway Fast Ethernet Hybrid ATA with FXS and FXO Ports
$39.99
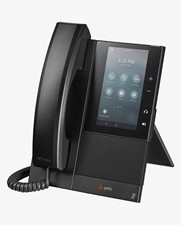
Poly CCX 505 Microsoft Teams Business IP Phone Touchscreen VoIP PoE Ethernet
$124.99
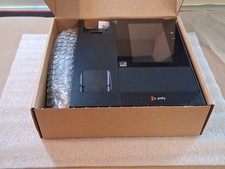
Poly CCX 400 Desktop Business Media Phone VoIP 2200-49700-019
$49.99
Viking Electronics VoIP Handsfree Emergency Phone E-1600-IP-EWP UPC 615687225778
$349.00
Cisco / Linksys SPA2102 VoIP 2FXS Phone Adapter with Router (unlocked)
$18.99
Yealink SIP-T87W Ultra Prime Business IP Phone WiFi Bluetooth VoIP Black New
$205.00
Ooma Phone Genie VoIP Home Phone Service - White (100-0474-100)
$22.50

Cisco/Linksys SPA2102 VoIP Phone Adapter Router 2FXS (Unlocked)
$17.99
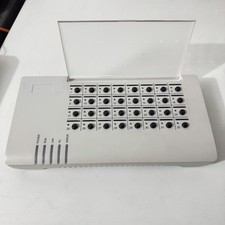
SIM Bank 32 SIM Card Slots Ethernet SIM Server for GoIP
$600.00
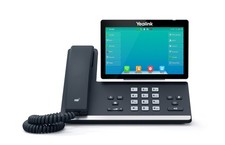
Yealink SIP-T57W-WITHPS 7" Touch IP Phone w/ Power Supply | New Sealed
$374.00
|
||
|
No Discussions have been posted on this vulnerability. |