|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Windows >> Quicktime < 7.0.4 (Windows) Vulnerability Assessment Details
|
Quicktime < 7.0.4 (Windows) |
||
|
Checks for Quicktime < 7.0.4 on Windows Detailed Explanation for this Vulnerability Assessment Summary : The remote version of QuickTime is affected by multiple code execution vulnerabilities. Description : The remote Windows host is running a version of Quicktime prior to 7.0.4. The remote version of Quicktime is vulnerable to various buffer overflows involving specially-crafted image and media files. An attacker may be able to leverage these issues to execute arbitrary code on the remote host by sending a malformed file to a victim and have him open it using QuickTime player. See also : http://lists.grok.org.uk/pipermail/full-disclosure/2006-January/041289.html http://lists.grok.org.uk/pipermail/full-disclosure/2006-January/041290.html http://lists.grok.org.uk/pipermail/full-disclosure/2006-January/041291.html http://lists.grok.org.uk/pipermail/full-disclosure/2006-January/041292.html http://lists.grok.org.uk/pipermail/full-disclosure/2006-January/041333.html http://lists.grok.org.uk/pipermail/full-disclosure/2006-January/041334.html http://lists.grok.org.uk/pipermail/full-disclosure/2006-January/041335.html http://www.cirt.dk/advisories/cirt-41-advisory.pdf http://lists.apple.com/archives/security-announce/2006/Jan/msg00001.html http://docs.info.apple.com/article.html?artnum=303101 Solution : Upgrade to Quicktime version 7.0.4 or later. Network Security Threat Level: High / CVSS Base Score : 7.0 (AV:R/AC:L/Au:NR/C:P/I:P/A:P/B:N) Networks Security ID: 16202 Vulnerability Assessment Copyright: This script is Copyright (C) 2006-2007 Tenable Network Security |
||
|
Cables, Connectors |
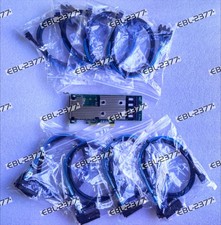
LSI 9305-16i SATA SAS 12Gbs Controller card PCIe 3.0 IT-Mode w/SAS SATA cable US
$109.98
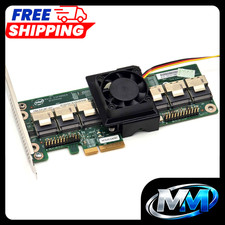
Intel RAID Expander RES2SV240 SAS 40mm Cooling Fan Included + Shroud Cooler
$31.95
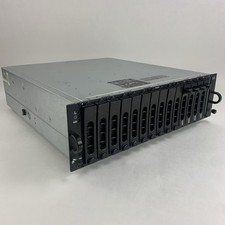
Dell PowerVault MD3000i AMP01 Storage Array 4x Cad 2x PSUs No HDDs/Controllers
$164.95
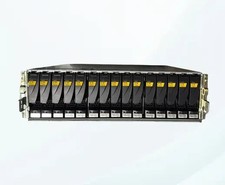
KTN-STL3 EMC VNX 15-slot Disk Array Expansion, full 15 x 2tb drives 100% health
$360.00
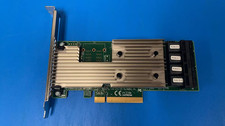
Broadcom LSI 9305-16i 12Gbps SAS-3 PCIe x8 HBA 16-Ports Raid Controller
$64.99
9300-8i LSI SAS3008 8-Port 12Gb PCIe IT mode ZFS FreeNAS unRAID 2*SFF-8643 US
$49.50
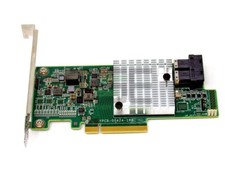
Inspur LSI SAS3008-i 8-Port 12Gb PCIe 3.0 SATA/SAS HBA IT Mode FreeNAS unRAID
$19.99
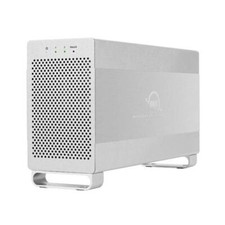
OWC Mercury Elite Pro 2 Bay RAID Enclosure with USB 3.2 for Dual 3.5 inch HDDs
$87.99
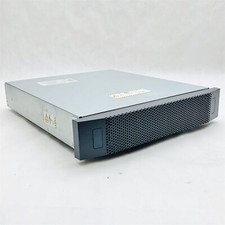
EMC VNXe3100 EPE 12-LFF 3.5" NAS Storage Array 12*3TB SAS HDD 2*303-137-000D
$224.99
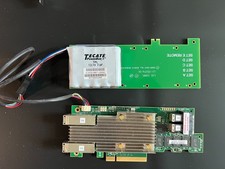
Broadcom LSI Avago RAID card MegaRAID SAS 9480-8i8e 05-50031-00
$400.00
|
||
|
No Discussions have been posted on this vulnerability. |