|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Windows >> Quicktime player buffer overflow Vulnerability Assessment Details
|
Quicktime player buffer overflow |
||
|
Checks the version of Quicktime Player Detailed Explanation for this Vulnerability Assessment The remote version of the Quicktime player is vulnerable to a buffer overflow. To exploit it, a possible hacker would need a user of this host to visit a rogue webpage with a malformed link in it. He could then be able to execute arbitrary code with the rights of the user visiting the page. Solution : Upgrade to Quicktime Player version 6.1 or later. Network Security Threat Level: High Networks Security ID: 7247 Vulnerability Assessment Copyright: This script is Copyright (C) 2003-2007 Tenable Network Security |
||
|
Cables, Connectors |
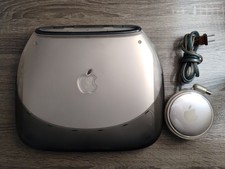
Vintage Apple iBook G3 Clamshell Graphite M2453 Mac OS 9 Working Charger Bundle
$199.99
Apple cloth fabric banner iBook tangerine orange New Old Stock Vintage
$99.00
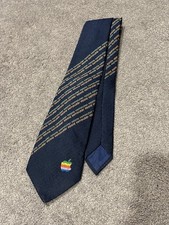
Vintage Apple Computer Logo Necktie - Extremely Rare
$250.00
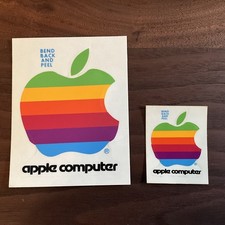
Lot of Original Vintage APPLE MACINTOSH Computer Rainbow Logo Stickers 2” And 4”
$10.99
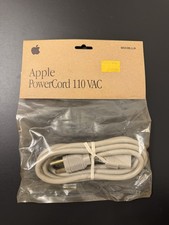
Vintage Apple PowerCord 110 VAC M5538LL/A Original Retail Packaging 1995
$32.00
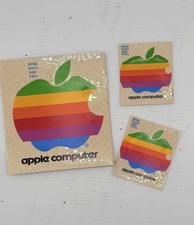
Lot of 3 VIntage Apple Computer Rainbow Logo Sticker Decal Macintosh 1980s NOS
$7.00
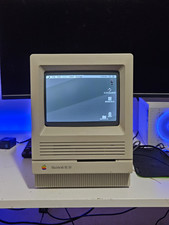
Apple Macintosh SE/30 Vintage Compact All-In-One CRT Desktop Computer M5119
$699.00
Apple Macintosh Color Classic Logic Board for Parts or Repair RARE Vintage
$75.00
Vintage Apple iBook A1005 12.1in White PowerPC G3 700MHz 128MB Mac OS X
$100.00
Vintage 1991 Apple Reference & Presentations Library v8.0 RESELLER EDITION RARE
$100.98
|
||
|
No Discussions have been posted on this vulnerability. |