|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Windows >> SMB log in Vulnerability Assessment Details
|
SMB log in |
||
|
Attempts to log into the remote host Detailed Explanation for this Vulnerability Assessment Summary : It is possible to logon on the remote host. Description : The remote host is running one of the Microsoft Windows operating system. It was possible to logon using one of the following account : - NULL session - Guest account - Given Credentials See also : http://support.microsoft.com/support/kb/articles/Q143/4/74.ASP http://support.microsoft.com/support/kb/articles/Q246/2/61.ASP Network Security Threat Level: none Networks Security ID: 494, 990, 11199 Vulnerability Assessment Copyright: This script is Copyright (C) 2005-2006 Tenable Network Security |
||
|
Cables, Connectors |
IBM 4262 SYSTEM x3200 Tower - HDD Wiped, NO OS
$80.00
IBM 7915 AC1 M4 E27R704 Server Intel 2650V2 32GB RAM NO HDD w/ 2x 750w PSU
$225.00
IBM QRadar xx29 2x Xeon E5-2650v4 2x 900W PSU M5120 12x 3.5" Bay Server No RAM
$149.99
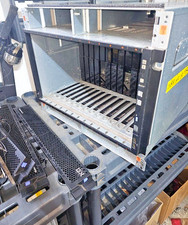
Lot of 2 IBM blade center Type H chassis 8852
$559.00
IBM System x3550 M3 1U Server 2x Xeon E5645, 192GB RAM, 2x 300GB HDD (7944-AC1)
$135.00
IBM Power S822 POWER8 1x CPU 32GB DDR4 RAM 2U Rack Server No HDD.
$629.99
IBM POWER8 8286-42A S824 16-Core 128GB RAM 4.8TB SAS Fedora Linux Server PowerVM
$750.00
IBM SYSTEM X3500 M3 SERVER 7380AC1 TOWER Server XEON E5620 8GB RAID SEE NOTES
$107.56
IBM ADP Server Type 7870 AC1 NO HDD | 128GB RAM PC3L | 2 x Xeon E5620
$189.99
DELL POWEREDGE HP IBM SERVER XEON GOLD 5415+ 8 CORE PROCESSOR 2.9 GHZ SRMGC
$1299.00
|
||
|
No Discussions have been posted on this vulnerability. |