|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> General >> Usable remote name server Vulnerability Assessment Details
|
Usable remote name server |
||
|
Acertains if the remote name server allows recursive queries Detailed Explanation for this Vulnerability Assessment Summary : The remote name server permits recursive queries to be performed by the host running nessusd. Description : It is possible to query the remote name server for third party names. If this is your internal nameserver, then forget this warning. If you are probing a remote nameserver, then it permits anyone to use it to resolve third parties names (such as www.nessus.org). This permits hackers to do cache poisoning attacks against this nameserver. If the host permits these recursive queries via UDP, then the host can be used to 'bounce' Denial of Service attacks against another network or system. See also : http://www.cert.org/advisories/CA-1997-22.html Solution : Restrict recursive queries to the hosts that should use this nameserver (such as those of the LAN connected to it). If you are using bind 8, you can do this by using the instruction 'permit-recursion' in the 'options' section of your named.conf If you are using bind 9, you can define a grouping of internal addresses using the 'acl' command Then, within the options block, you can explicitly state: 'permit-recursion { hosts_defined_in_acl }' For more info on Bind 9 administration (to include recursion), see: http://www.nominum.com/content/documents/bind9arm.pdf If you are using another name server, consult its documentation. Network Security Threat Level: Medium / CVSS Base Score : 4 (AV:R/AC:L/Au:NR/C:N/A:N/I:P/B:I) Networks Security ID: 136, 678 Vulnerability Assessment Copyright: This script is Copyright (C) 2005 Tenable Network Security |
||
|
Cables, Connectors |
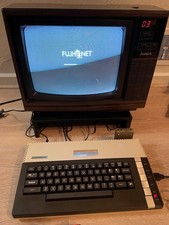
Fujinet 1.7.1 Atari 400 800 800XL 130XE 65XE XEGS Assembled, Tested, Working
$99.99
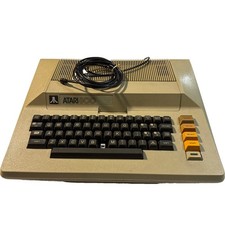
Atari 800 Home Computer For Parts Repair Untested Power Cord
$124.92
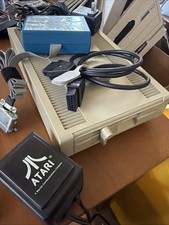
ATARI XF551 DISK DRIVE WITH AC POWER ADAPTER AND PARALLEL PORT ADAPTER, UNTESTED
$250.00
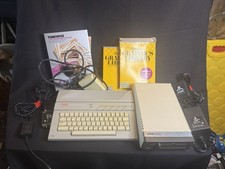
Atari 130 XE/Atari 1050 Bundle W/ Cords And Extras (Powered On)
$300.00
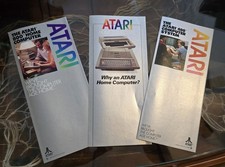
Vintage Atari 400/800 Home Computer Brochures – Set of 3 – $20
$20.00
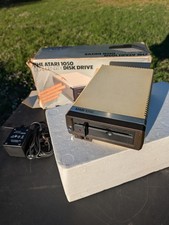
Vintage Atari 1050 Floppy Disk Drive w/ Power Adapter *Parts Only
$49.00
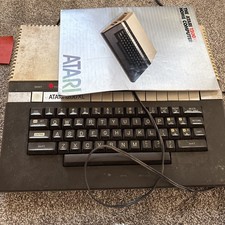
Vintage Atari 1200XL Home Computer Powers On, w owners guide and power supply
$250.00
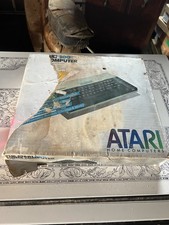
Atari 800 Xl Home Computer Untested In Box 800xl Vintage
$125.00
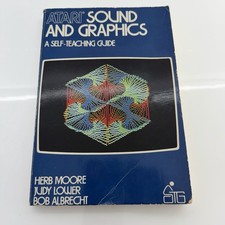
ATARI SOUND & GRAPHICS Self Teaching Guide 400/800/1200XL/130XE/XEGS/800XL/600XL
$20.00
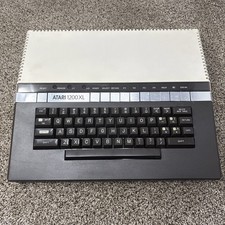
Atari 1200XL Computer Game Console Vintage Rare BAD KEYBOARD MYLAR
$275.00
|
||
|
No Discussions have been posted on this vulnerability. |