|
|
Vulnerability Assessment & Network Security Forums |
|||||||||
|
If through a vulnerability assessment, a network security issue is detected for the vulnerability below, applying the appropriate security patches in a timely matter is very important. If you have detected that your system has already been compromised, following CERT's Network Security recovery document will assist with recommended steps for system recovery. Home >> Browse Vulnerability Assessment Database >> Backdoors >> mstream handler Detect Vulnerability Assessment Details
|
mstream handler Detect |
||
|
Detects the presence of a mstream agent Detailed Explanation for this Vulnerability Assessment The remote host appears to be running a mstream handler, which is a trojan that can be used to control your system or make it attack another network (this is actually called a distributed denial of service attack tool) It is very likely that this host has been compromised Solution : Restore your system from backups, contact CERT and your local authorities Network Security Threat Level: Critical Networks Security ID: Vulnerability Assessment Copyright: This script is Copyright (C) 2000 Renaud Deraison |
||
|
Cables, Connectors |
TP-Link TL-SG105 5-Port Gigabit Ethernet Unmanaged Metal Desktop Network Switch
$17.99
NETGEAR GS308EP Essential Series 8-Port Gigabit PoE+ Unmanaged Switch
$39.99
D-Link DGS-1210-28P 28-Port PoE Gigabit Web Smart Switch With Cord
$49.99
5Ports Gigabit Network Switch w/ 4 PoE+ Ports Total 52W each port 30W Plug&Play
$31.99
Monoprice 5-Port 10/100/1000Mbps Gigabit Ethernet Unmanaged Switch Network Hub
$8.99
8 Port 2.5Gb Ethernet Switch Unmanaged Network Switch w/8 x 2.5G & 1 x 10G SFP
$45.00
TP-Link TL-SG2210P 10-Port Gigabit Smart Switch w/ 8-Port PoE+ NO AC SKU 25597
$36.98
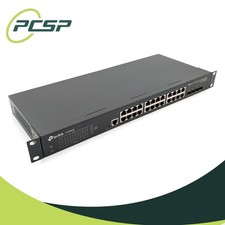
TP-Link Omada SG3428 24-Port Gigabit L2+ Managed Switch 4x SFP w/ Ears
$99.99
TP-Link TL-SG1016 16-Port Gigabit Ethernet Unmanaged Rackmount Switch
$39.99
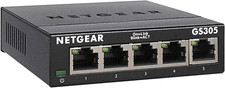
NETGEAR 5-Port Gigabit Ethernet Unmanaged Switch (Gs305) - Desktop Quiet Fanless
$22.00
|
||
|
No Discussions have been posted on this vulnerability. |